Salesforce-MuleSoft-Platform-Architect Exam Questions With Explanations

The best Salesforce-MuleSoft-Platform-Architect practice exam questions with research based explanations of each question will help you Prepare & Pass the exam!
Over 15K Students have given a five star review to SalesforceKing
Why choose our Practice Test

By familiarizing yourself with the Salesforce-MuleSoft-Platform-Architect exam format and question types, you can reduce test-day anxiety and improve your overall performance.

Up-to-date Content

Ensure you're studying with the latest exam objectives and content.

Unlimited Retakes

We offer unlimited retakes, ensuring you'll prepare each questions properly.

Realistic Exam Questions

Experience exam-like questions designed to mirror the actual Salesforce-MuleSoft-Platform-Architect test.

Targeted Learning

Detailed explanations help you understand the reasoning behind correct and incorrect answers.

Increased Confidence

The more you practice, the more confident you will become in your knowledge to pass the exam.

Study whenever you want, from any place in the world.
Salesforce Salesforce-MuleSoft-Platform-Architect Exam Sample Questions 2026

Start practicing today and take the fast track to becoming Salesforce Salesforce-MuleSoft-Platform-Architect certified.

21524 already prepared
Salesforce 2026 Release
152 Questions
4.9/5.0

An Anypoint Platform organization has been configured with an external identity provider (IdP) for identity management and client management. What credentials or token must be provided to Anypoint CLI to execute commands against the Anypoint Platform APIs?

A. The credentials provided by the IdP for identity management

B. The credentials provided by the IdP for client management

C. An OAuth 2.0 token generated using the credentials provided by the IdP for client management

D. An OAuth 2.0 token generated using the credentials provided by the IdP for identity management

D.   An OAuth 2.0 token generated using the credentials provided by the IdP for identity management

Explanation:

When an Anypoint Platform organization is configured with an external identity provider (IdP), authentication and authorization are delegated to that IdP. This means that both users and clients authenticate against the IdP rather than directly against Anypoint’s native identity system.

For tools such as Anypoint CLI, which execute commands against the Anypoint Platform APIs, the CLI must authenticate using an OAuth 2.0 token. This token is generated by the IdP and represents the authenticated user’s identity and permissions.

Key points:
- Identity management via IdP: The IdP issues OAuth 2.0 tokens for users. These tokens are then used by Anypoint CLI to call Anypoint Platform APIs.
- Client management via IdP: This applies to API client applications (e.g., apps consuming APIs via Client ID/Secret). It is not relevant for CLI authentication, which requires user identity tokens.
- OAuth 2.0 token usage: The CLI does not use raw credentials (username/password) directly. Instead, it requires a valid OAuth 2.0 token issued by the IdP.
- Why identity management, not client management: CLI commands are executed on behalf of a user, not an API client application. Therefore, the token must come from the IdP’s identity management flow, not client management.

This aligns with MuleSoft’s best practices:
- CLI authentication → OAuth 2.0 token from IdP (identity management).
- API client authentication → Client ID/Secret from IdP (client management).

Thus, the correct answer is Option D, because the CLI requires an OAuth 2.0 token generated using IdP credentials for identity management.

❌ Option A
The credentials provided by the IdP for identity management — Incorrect. Raw credentials (username/password) are not used directly; they must generate an OAuth 2.0 token.

❌ Option B
The credentials provided by the IdP for client management — Incorrect. These are for API client applications, not CLI user authentication.

❌ Option C
An OAuth 2.0 token generated using the credentials provided by the IdP for client management — Incorrect. This applies to API clients, not CLI users. CLI requires identity tokens.

📖 References:
MuleSoft Documentation: External Identity Providers
MuleSoft Documentation: Anypoint CLI Authentication
MuleSoft Certified Platform Architect I Exam Guide — Identity and Access Management section

👉 In summary:
Option D is correct because Anypoint CLI requires an OAuth 2.0 token from the IdP’s identity management flow, not client management credentials.

A company has created a successful enterprise data model (EDM). The company is committed to building an application network by adopting modern APIs as a core enabler of the company's IT operating model. At what API tiers (experience, process, system) should the company require reusing the EDM when designing modern API data models?

A. At the experience and process tiers

B. At the experience and system tiers

C. At the process and system tiers

D. At the experience, process, and system tiers

C.   At the process and system tiers

Explanation:

An Enterprise Data Model (EDM), or Canonical Data Model, is used to standardize the data format across an organization's systems to ensure consistency and reusability. In the context of MuleSoft's API-led connectivity approach:

System APIs should expose the core data from the systems of record, often in a normalized, canonical format. This insulates consumers from the underlying system's proprietary data structures and ensures a consistent foundation for all data within the organization.
Process APIs are where the business logic is implemented, orchestrating and shaping data by interacting with multiple System APIs. They consume and produce data based on the canonical format to ensure consistency across business processes.
Experience APIs, however, are designed specifically for the end consumer (e.g., mobile app, web portal) and their unique needs. The data model for an Experience API is typically tailored to the user experience, meaning it might combine, simplify, or reformat data from the underlying Process APIs. This is a deliberate step away from the standardized EDM to optimize for a specific consumer. Therefore, reusing the EDM at the Experience layer would be a poor practice as it would not be optimized for the consumer's needs.

In summary, the EDM is critical for establishing a consistent data language at the foundational and intermediate layers (System and Process) but is intentionally abstracted and transformed at the consumer-facing layer (Experience).

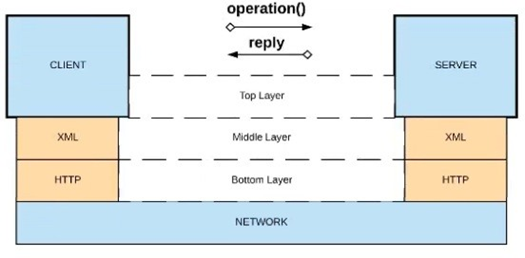
Refer to the exhibit.


What is a valid API in the sense of API-led connectivity and application networks?

A) Java RMI over TCP
B) Java RMI over TCP
C) CORBA over HOP
D) XML over UDP

A. Option A

B. Option B

C. Option C

D. Option D

B.   Option B

Explanation:

Protocol Standard: API-led connectivity emphasizes the use of HTTP-based protocols (like REST/JSON or XML over HTTP). These protocols are lightweight, platform-independent, and universally understood by modern web and mobile applications.

Governance and Management: Using HTTP allows the Anypoint Platform to easily apply standard policies (such as OAuth 2.0, rate limiting, and threat protection) to the traffic. Legacy protocols like RMI or CORBA do not support this level of centralized governance without significant custom wrapping.

Discoverability and Reuse: Application networks thrive on Self-Service. HTTP-based APIs can be easily documented in RAML/OAS and published to Anypoint Exchange, where developers can discover and test them using a browser.

Incorrect Answers
A & B. Java RMI over TCP
❌ Remote Method Invocation (RMI) is a language-specific protocol (Java-only) that requires both the client and server to share the same object model. This creates tight coupling and prevents reuse by non-Java applications, which violates the core principle of an open application network.

C. CORBA over IIOP
❌ CORBA is a legacy distributed object architecture. While it was intended for interoperability, it is notoriously complex to implement and manage. It does not align with the modern "lightweight building block" philosophy of API-led connectivity.

D. XML over UDP
❌ UDP is a connectionless, unreliable transport protocol. APIs in an application network require reliable delivery and standard request-response semantics (provided by TCP/HTTP) to ensure transactional integrity and proper error handling.

Reference
Source: MuleSoft: What is API-led Connectivity?

Key Concept:
Modern APIs. MuleSoft distinguishes between "Connectivity" (the technical pipe) and a "Modern API." A modern API is designed for a specific consumer, is easily discoverable, and is built on open standards like HTTP and JSON/XML to facilitate the creation of a composable application network.

Which of the following sequence is correct?

A. API Client implementes logic to call an API >> API Consumer requests access to API >> API Implementation routes the request to >> API

B. API Consumer requests access to API >> API Client implementes logic to call an API >> API routes the request to >> API Implementation

C. API Consumer implementes logic to call an API >> API Client requests access to API >> API Implementation routes the request to >> API

D. API Client implementes logic to call an API >> API Consumer requests access to API >> API routes the request to >> API Implementation

B.   API Consumer requests access to API >> API Client implementes logic to call an API >> API routes the request to >> API Implementation

Explanation:

The process follows this logical order:

API Consumer requests access to API: An organization or developer (the API consumer) discovers an API in Anypoint Exchange and requests access. This usually involves obtaining client credentials (Client ID and Secret) to use the API.

API Client implements logic to call an API: The developer then incorporates the API call into their application's code (the API client). This involves programming the application to use the obtained credentials and send requests to the API's endpoint.

API routes the request to API Implementation: At runtime, the implemented API client makes a request. The API Gateway (the "API" in the sequence) intercepts this request, validates the credentials and applies policies, and then routes the traffic to the backend Mule application (the API implementation) that contains the business logic.

Why other options are incorrect:

A: This sequence is incorrect because the consumer must first request access and obtain credentials before the client can implement the logic to call the API.

C: This option swaps the roles of "Consumer" and "Client." The consumer is the entity (person/organization) requesting access, while the client is the software component making the actual programmatic call.

D: Similar to A, access must be granted before implementation can begin. Also, the roles are slightly jumbled at the end, as the API (Gateway/Proxy) routes the request to the implementation.

An API implementation is being designed that must invoke an Order API, which is known to repeatedly experience downtime. For this reason, a fallback API is to be called when the Order API is unavailable. What approach to designing the invocation of the fallback API provides the best resilience?

A. Search Anypoint Exchange for a suitable existing fallback API, and then implement invocations to this fallback API in addition to the Order API

B. Create a separate entry for the Order API in API Manager, and then invoke this API as a fallback API if the primary Order API is unavailable

C. Redirect client requests through an HTTP 307 Temporary Redirect status code to the fallback API whenever the Order API is unavailable

D. Set an option in the HTTP Requester component that invokes the Order API to instead invoke a fallback API whenever an HTTP 4xx or 5xx response status code is returned from the Order API

A.    Search Anypoint Exchange for a suitable existing fallback API, and then implement invocations to this fallback API in addition to the Order API

Explanation:

✅ Why A is correct:
For maximum resilience, MuleSoft recommends handling fallback logic explicitly in the application flow, rather than relying on implicit platform behavior or redirects.

A resilient design typically includes:
- Primary API invocation
- Explicit error handling / circuit-breaker logic
- Fallback API invocation when the primary API fails

By searching Anypoint Exchange for an existing fallback or alternative API (e.g., a cached, degraded, or read-only service) and invoking it when the primary Order API is unavailable, you:
- Maintain control over fallback behavior
- Avoid tight coupling or hidden runtime behavior
- Align with API-led connectivity and reuse principles

This is the most reliable and architecturally correct approach.

❌ Why the other options are incorrect:

B. Create a second API in API Manager and invoke it as fallback
API Manager is for governance and policy enforcement, not dynamic fallback routing. Creating a second API instance does not inherently provide resilience.

C. Redirect using HTTP 307
Redirecting clients pushes responsibility to the consumer and breaks abstraction. Clients may not support or expect redirects, which violates good API design practices.

D. Use an HTTP Requester option to auto-fallback
The Mule HTTP Requester does not provide a built-in fallback option for handling 4xx/5xx responses. Error handling and fallback logic must be explicitly implemented in the flow using patterns like on-error-continue, choice, or circuit breaker.

✅ Summary:
The most resilient and MuleSoft-aligned approach is to explicitly design fallback behavior in the application logic, typically using an alternative API discovered via Anypoint Exchange.

Prep Smart, Pass Easy Your Success Starts Here!

Transform Your Test Prep with Realistic Salesforce-MuleSoft-Platform-Architect Exam Questions That Build Confidence and Drive Success!