


B2C-Commerce-Architect Exam Questions With Explanations
The best B2C-Commerce-Architect practice exam questions with research based explanations of each question will help you Prepare & Pass the exam!

Over 15K Students have given a five star review to SalesforceKing

Why choose our Practice Test
By familiarizing yourself with the B2C-Commerce-Architect exam format and question types, you can reduce test-day anxiety and improve your overall performance.
Up-to-date Content
Ensure you're studying with the latest exam objectives and content.
Unlimited Retakes
We offer unlimited retakes, ensuring you'll prepare each questions properly.
Realistic Exam Questions
Experience exam-like questions designed to mirror the actual B2C-Commerce-Architect test.
Targeted Learning
Detailed explanations help you understand the reasoning behind correct and incorrect answers.
Increased Confidence
The more you practice, the more confident you will become in your knowledge to pass the exam.
Study whenever you want, from any place in the world.

Salesforce B2C-Commerce-Architect Exam Sample Questions 2026
Start practicing today and take the fast track to becoming Salesforce B2C-Commerce-Architect certified.
2644 already prepared
Salesforce 2026 Release64 Questions
4.9/5.0
An Order Management System (OMS) handles orders from multiple brand specific sites, as part of the processing, the OMS sends the processing detail to be added at notes to the orders in B2C Commerce. These processing details are captured temporarily in custom objects, and are later processed by a batch Job that:
• Processes the custom object to extract the orderid and note data.
• Tries to load the order.
• If the order is not found, it deletes the custom object and moves on.
• If the order is found, it updates notes In the Order, upon successful update of this order, it deletes the custom object.
There is an Issue reported that the job is constantly failing and custom objects are growing in number. On investigating the production look the message below is being logged on each failure:
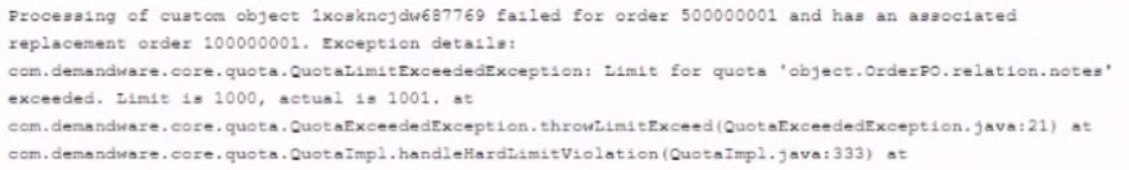
What are three solution The Architect can take to fix this issue without losing meaningful data? (Choose 2 answers)
A. Take the backup of the Order as XML and delete the Order to ensure on the next job run, the custom objects are getting processed.
B. Using BM site import/export, soften the
C. Take the backup of the custom object and delete the custom object to ensure on the next job run the custom objects are getting processed.
D. Engage B2C Commerce Support Team to soften the quota limit for ‘’object.OrderPO.relation.notes’’
E. Take the backup of the Order as XML and delete the notes from Order to ensure on the next job run the custom objects are getting processed.
Explanation:
A. Take the backup of the Order as XML and delete the Order…
Deleting the entire order just to fix note count is too destructive. Orders are legal, accounting, and customer data — removing them breaks record-keeping and reporting. This is not a valid solution.
✅ Eliminate
B. Using BM site import/export, soften the warn to make sure that neither order notes are lost and custom object is processed.
You cannot “soften” quota errors via Business Manager. A QuotaLimitExceededException is a hard platform limit — not just a warning you can silence in settings or an import/export tweak.
✅ Eliminate
C. Take the backup of the custom object and delete the custom object to ensure on the next job run the custom objects are getting processed.
This would delete the custom object before it can be retried, but that’s not helpful because it loses the meaningful order notes data that the OMS wanted to save. The data would be gone and never written to the order.
✅ Eliminate
D. Engage B2C Commerce Support Team to soften the quota limit for ‘object.OrderPO.relation.notes’.
This is valid. Quotas are sometimes adjustable via Salesforce Support. While some quotas are hard-coded, many object relation quotas can be raised if justified. It’s definitely one avenue an Architect should consider if the business has a legitimate case for storing >1000 notes.
✅ Correct
E. Take the backup of the Order as XML and delete the notes from Order to ensure on the next job run the custom objects are getting processed.
This is practical. Export the order for safekeeping, then remove older or unneeded notes to bring the total below the limit. This frees up quota for new notes to be written, allowing the custom objects to be processed. Data can be re-imported if needed.
✅ Correct
During implementation, the team found that there is a notification controller exposed for an external service that marks the order as paid when notification is received. The notification URL is sent to the service together with the payment request and contains only the URL with orderlD as the parameter. What should the Architect recommend to the team in order to prevent the unauthorized usage of the controller to mark the orders as paid?
A. Add a customer number in the callback URL and match the customer number against the one stored on the order.
B. Add HTTPSrestriction to the controller start node.
C. Add an order token in the callback URL and match the token against the one stored on the order.
D. Add a session attribute and validate it on the callback.
Explanation:
✅ Why these options are correct?
✅ Option C: Add an order token in the callback URL and match the token against the one stored on the order.
Explanation:
Adding an order token to the callback URL is a highly recommended security measure to prevent unauthorized usage of the notification controller. The token is a unique, temporary identifier that ensures the callback is legitimate and comes from the right source. By matching the token in the callback URL against the one stored with the order, you can securely verify that the notification is valid and authorized to mark the order as paid. This approach ensures that only the correct external service can trigger the payment confirmation for the order.
❌ Why these options are incorrect?
❌ Option A: Add a customer number in the callback URL and match the customer number against the one stored on the order.
Explanation:
While this may seem like a valid approach, matching the customer number against the order doesn't provide a strong security measure because the customer number might be easily accessible or guessable. If an attacker knows the customer number, they could send a request that marks the order as paid, which doesn’t provide robust protection. Additionally, customer numbers are not as unique or as secure as a token specifically generated for each order.
❌ Option B: Add HTTPS restriction to the controller start node.
Explanation:
While using HTTPS is a good security practice to encrypt the communication between the client and server, it doesn’t directly prevent unauthorized usage of the notification URL. HTTPS ensures data encryption but doesn't inherently provide validation mechanisms to verify whether the incoming request is from a legitimate source. Without a form of validation (such as an order token), an attacker could still potentially send a valid-looking request and mark orders as paid.
❌ Option D: Add a session attribute and validate it on the callback.
Explanation:
Session attributes are typically associated with user sessions on the storefront and are less relevant for validating external service requests. Since the callback comes from an external service, the session attribute won't be available to validate the callback properly. This approach is more suited for user-driven actions on the site, rather than for validating an external service interaction.
The storefront integrates with a REST based Address verification service (AVS) that uses token based security. The sequence of calls in the API documentation for this AVS looks like the following
1. Client authentication call, which contains the merchantId and secret in a GET request and returns a token in the response.
2. Address verification call, which contains the token and the address to verify in a POST request.
Once the token is obtained, it is valid for hours and it is not needed to request a new one for subsequent address verification calls, the AVS charges for every request made no matter if it is client authentication call or address verification call.
Which three strategies could be applied to allow for efficient use of the service without compromising security?
(Choose 3 answers)
A. Apply page caching to the client authentication controller that is used with AJAX.
B. Obtain the token from local storage of the browser and update it once It expires.
C. Obtain the token from a custom cache before making the client authentication call.
D. Use HTTPService caching for the client authentication call.
E. Use a job to store and update the token in a custom object that is used from the storefront code
D. Use HTTPService caching for the client authentication call.
E. Use a job to store and update the token in a custom object that is used from the storefront code
Explanation:
✅ Option C: Obtain the token from a custom cache before making the client authentication call.
Reasoning:
This is an optimal strategy. By storing the token in a custom cache on the server side, the system can check the cache for an existing valid token before making the client authentication call. This avoids unnecessary requests to the AVS service, reducing cost and improving efficiency. Tokens can be cached with an expiration time, ensuring that expired tokens are updated automatically.
✅ Option D: Use HTTPService caching for the client authentication call.
Reasoning:
HTTPService caching can indeed be used to cache the token that comes from the client authentication call. This is another way of avoiding repeated requests to the AVS service, which would cost more. The token can be cached for the duration of its validity and reused across subsequent calls. It makes the process more efficient as it minimizes redundant requests to the AVS service.
✅ Option E: Use a job to store and update the token in a custom object that is used from the storefront code.
Reasoning:
A scheduled job to periodically store and update the token in a custom object is also a good strategy. This approach is helpful if you want to manage token expiry efficiently. The job can check if the token has expired and refresh it when necessary. This method is ideal for ensuring that the storefront always has access to a valid token without making redundant client authentication calls.
❌ Option A: Apply page caching to the client authentication controller that is used with AJAX.
Reasoning:
Page caching in this case is not ideal. Since the client authentication call returns a unique token per session (likely specific to each customer), caching it would result in inappropriate reuse of tokens across different users, which would compromise security. Tokens are typically sensitive and session-specific, so caching them at the page level is not secure.
❌ Option B: Obtain the token from local storage of the browser and update it once it expires.
Reasoning:
Storing the token in local storage on the client side is risky and insecure. Local storage is vulnerable to cross-site scripting (XSS) attacks, meaning a malicious user could potentially steal the token. Also, local storage doesn’t have the same security protections that server-side storage or session storage does. It’s better to manage tokens server-side where they can be better protected.
A new version of the Page Show controller is required for implementation of Page Deserter
specific look. It requires implementation of a specific, cache period for Page Designer pages, which b not currently available in the base Storefront Reference Architecture (SFRA) cache.js module.
What two steps should the Architect instruct the developer to implement?
(Choose 2 answers)
A. Create new Page.js controller in client s cartridge. Copy code from base and modify the Page-Show route to include the new cache middleware function.
B. Create new ceche,js client's cartridge. Copy cache,js from app_storefront_base and add a function for the Page Designer caching.
C. Create new Page,js controller in client's cartridge. Extend the code from base and prepend the new cache middleware function to Page-Show route.
D. Create new cache,js in client's cartridge. Extend cache,js from app_storefront_baseand adda function for the Page Designer caching.
Explanation:
The client wants a Page Designer-specific cache period, which SFRA’s base cache.js does not provide. The best practice is to extend, not copy, the base modules.
Why C is correct:
Extend the base Page.js controller instead of replacing it. Use server.prepend to add the custom cache middleware to the Page-Show route without duplicating code.
Example:
'use strict';
var server = require('server');
server.extend(module.superModule);
var cache = require('*/cartridge/scripts/middleware/cache');
server.prepend(
'Show',
cache.cachePageDesigner
);
module.exports = server.exports();
Why D is correct:
Instead of copying the entire cache.js file, extend it and add a new function for Page Designer caching. This approach is safer for upgrades and avoids duplication.
Example:
var base = require('app_storefront_base/cartridge/scripts/middleware/cache');
module.exports = {
...base,
cachePageDesigner: base.custom({
mode: 'server',
expires: 300
})
};
Why A and B are incorrect:
Copying entire controllers or scripts increases technical debt and maintenance costs. It’s better to extend existing modules to stay compatible with future SFRA upgrades.
A third party survey provider offers both an API endpoint for individual survey data and an SFTP server endpoint that can accept batch survey data. The initial implementation of the integration includes
1. Marking the order as requiring a survey before order placement
2. On the order confirmation pace, the survey form is displayed for the customer to fill
3. The data is sent to the survey provider API, and the order it marked as not requiring a survey
Later it was identified that this solution is not fit for purpose as the following issues and additional requirements were identified:
1. If the API call fails, the corresponding survey data is lost. The Business requires to avoid data loss.
2. Some customers skipped the form. The Business require sending a survey email to such customers.
3. The Order Management System (OMS) uses a non-standard XML parser it did not manage to parse orders with the survey, until the survey attribute was manually removed from the xml.
How should the Architect address the issues and requirements described above?
A. Create a custom session attribute when the survey is required. Send to the API endpoint in real-time. On failure, capture the survey data in the session and reprocess, use me session attribute to send emails for the cases when survey was skipped.
B. Create a custom object to store the survey data. Send to the API endpoint using a job. On success, remove the custom object. On failure, send the survey data with API from the next execution of the same job. Use the custom object to send emails for the cases when the survey was skipped.
C. Create a custom object when the survey is required Send to the API endpoint in real- time. On success, remove the object. On failure, capture the survey data in the custom object and later reprocess with a job. Use the custom object to send emails for the cases when survey was skipped.
D. Send the survey data to the API endpoint in real-time until the survey data is successfully captured. Instruct the OMS development team to update their XML parser, use the Order survey attribute to send emails for the cases when the survey was skipped.
Explanation:
Why Option B?
✅ Persistent Storage (Custom Object) for Survey Data
Ensures no data loss if the API fails (stores survey responses reliably).
Batch processing via a job improves reliability (retries failed submissions).
✅ Handles Skipped Surveys (Email Fallback)
The custom object tracks which customers skipped the survey, enabling email follow-ups.
✅ Avoids OMS XML Parsing Issues
Since the survey data is stored separately (not embedded in the order XML), it prevents OMS parsing failures.
Why Not Other Options?
❌ A. Session-based storage
Session data is volatile (lost if the user leaves or the session expires).
Not reliable for retries or email follow-ups.
❌ C. Hybrid (Real-time + Job)
Real-time API calls can still fail, requiring retries.
Less efficient than a pure batch/job approach (Option B).
❌ D. Force real-time retries + OMS parser update
Does not guarantee data persistence (if API keeps failing).
Depends on OMS changes (out of the Architect’s control).
Best Practice & Reference:
Use Custom Objects for transient but critical data (e.g., surveys).
Batch jobs (instead of real-time) for resilient third-party integrations.
Salesforce B2C Commerce recommends asynchronous processing for reliability.
Prep Smart, Pass Easy Your Success Starts Here!
Transform Your Test Prep with Realistic B2C-Commerce-Architect Exam Questions That Build Confidence and Drive Success!


