Last Updated On : 18-Nov-2026
Salesforce Platform Developer - Plat-Dev-201 Practice Test
Prepare with our free Salesforce Platform Developer - Plat-Dev-201 sample questions and pass with confidence. Our Salesforce-Platform-Developer practice test is designed to help you succeed on exam day.
Salesforce 2026
A developer is working on a project to import data from an external system into Salesforce. The data contains sensitive information that should not be visible to all users in Salesforce. What should the developer do to ensure that the data is secure?
A. Use the Salesforce CLI to import the data and set up user permissions to restrictaccess to sensitive data.
B. Use the Apex Data Loader to import the data and write Apex code to handle securityand access control
C. Use a third-party tool to encrypt the sensitive data before importing it into Salesforce
D. Use the Data Import Wizard to import the data and set up field-level security torestrict access to sensitive fields
Explanation:
For securing sensitive data so that it is not visible to all users, Salesforce's standard, native security mechanism is Field-Level Security (FLS), configured through Profiles and/or Permission Sets. FLS allows an administrator or developer to control, at a granular level, which specific fields each user can view and/or edit, ensuring sensitive fields are hidden from users who should not have access, regardless of their overall object-level access.
The Data Import Wizard is a standard, supported, point-and-click tool for importing data, including Accounts, Contacts, Leads, and custom objects, into Salesforce without requiring custom code. Combining it with properly configured Field-Level Security addresses both:
1. Getting the external data into Salesforce through a supported, native tool.
2. Ensuring only appropriate users can view or access the sensitive fields after the data is imported, which directly satisfies the stated business requirement.
This represents the correct application of Salesforce's built-in, declarative security model and is the recommended first approach before resorting to custom code or external tools.
Why the other options are wrong:
A. Use the Salesforce CLI to import the data and set up user permissions to restrict access to sensitive data.
While Salesforce CLI can be used for data import and general user permissions through Profiles and Permission Sets play a role in security, this option is vaguer and less precise. It does not specifically identify Field-Level Security, which is the appropriate mechanism for restricting access to particular sensitive fields rather than broader object-level or system permissions.
B. Use the Apex Data Loader to import the data and write Apex code to handle security and access control.
Writing custom Apex code to manage security and access control is unnecessary and is not a best practice when Salesforce provides robust, native, declarative security features such as Field-Level Security, sharing rules, Profiles, and Permission Sets. Introducing custom code adds unnecessary complexity, maintenance overhead, and potential security risks compared with using the platform's built-in security model.
C. Use a third-party tool to encrypt the sensitive data before importing it into Salesforce.
Encrypting data before import introduces unnecessary complexity and does not align with Salesforce's native security capabilities. It would also complicate the ability to use, report on, or search the data normally within Salesforce. Salesforce also offers native Shield Platform Encryption when field-level encryption is truly required, but that is a separate consideration from basic access restriction, which Field-Level Security handles directly.
Reference
Field-Level Security - Salesforce Help
Data Import Wizard - Salesforce Help
A developer creates a Lightning web component that imports a method within an Apex class. When a Validate button is pressed, the method runs to execute complex validations. In this implementation scenario, which two options are part of the Controller according to the MVC architecture? Choose 2 answers
A. JavaScript file
B. XML file
C. Apex class
D. HTML file
C. Apex class
Explanation:
A. Reuse the event logic in a component bundle, by putting the logic in the helper:
Correct. In Aura components, placing reusable event-handling logic in the helper promotes code reuse and keeps the event handlers focused on handling the event and delegating the appropriate logic.
B. Handle low-level events in the event handler and re-fire them as higher-level events:
Correct. A component can handle a lower-level event and then fire a higher-level event when appropriate. This helps separate the implementation details of a component from the broader communication between components.
Why the other options are incorrect
C. Try to use application events as opposed to component events:
Incorrect. Application events should not be preferred by default. Component events are generally preferred for communication between components in the containment hierarchy. Application events should be used when components that are not directly related need to communicate.
D. Use component events to communicate actions that should be handled at the application level:
Incorrect. If an action needs to be handled at the application level, an application event is more appropriate. Component events are intended for communication within the component hierarchy.
Key Exam Point
Component event: communication between components in the component hierarchy.
Application event: communication across components that may not have a direct containment relationship.
Put reusable event logic in the helper.
Low-level events can be transformed into higher-level events.
Answer: A and B
What should a developer use to fix a Lightning web component bug in a sandbox?
A. Force.com IDE
B. Execute Anonymous
C. Developer Console
D. VS Code
Explanation:
VS Code, combined with the Salesforce Extension Pack, which includes Salesforce CLI/DX integration, is the standard, Salesforce-recommended tool for developing, editing, and debugging Lightning Web Components. It provides:
Full LWC syntax support, IntelliSense, and code completion for JavaScript, HTML, and CSS files that make up an LWC bundle.
The ability to push and pull source between the local project and a sandbox or scratch org.
Integrated debugging tools, linting with ESLint, and Jest test support for LWC unit testing.
Direct integration with Salesforce DX for deploying and retrieving metadata, including LWC bundles, to and from a sandbox.
Why the other options are wrong:
A. Force.com IDE:
This is a deprecated, legacy Eclipse-based IDE that Salesforce no longer actively supports or recommends for modern development. It predates Lightning Web Components and does not support LWC development.
B. Execute Anonymous:
This is a feature within the Developer Console, or VS Code, used to run ad-hoc Apex code snippets for testing and debugging purposes. It has no relevance to editing or fixing Lightning Web Component JavaScript, HTML, or CSS bugs.
C. Developer Console:
The Developer Console is browser-based and primarily supports Apex classes and triggers, Visualforce pages, and Aura components. It does not support editing Lightning Web Components. LWC files are not accessible or editable through the Developer Console's interface, making it unsuitable for this task.
Reference
Set Up Visual Studio Code - Lightning Web Components Developer Guide | Salesforce Extensions for VS Code
Which two Agentforce limitations should a developer consider when building an agent?
A. Custom actions that reference an Apex class or flow support only primitive data types.
B. The Agent API has a 90-second timeout.
C. Inbound messages sent via messaging channels have character limits
D. Version control is supported for agents
C. Inbound messages sent via messaging channels have character limits
Explanation:
A. Custom actions that reference an Apex class or Flow support only primitive data types:
Correct. When building Agentforce custom actions that use Apex or Flow, developers need to consider the supported input and output data types. The action interface has limitations around complex data types, which can affect how the action is designed.
C. Inbound messages sent via messaging channels have character limits:
Correct. Messaging channels impose limits on the size of inbound messages. Developers need to account for these limits when designing agents that process customer messages.
Why the other options are incorrect
B. The Agent API has a 90-second timeout:
Incorrect. A 90-second timeout is not the relevant Agentforce limitation described for this question.
D. Version control is supported for agents:
Incorrect. This is not a limitation. Salesforce provides mechanisms for managing and deploying agent configurations, but the statement itself does not describe a limitation developers need to consider.
Key Exam Point
When developing Agentforce agents, pay attention to action data-type limitations and messaging-channel character limits, because both can affect how an agent and its integrations are designed.
What is the result of the following code snippet?
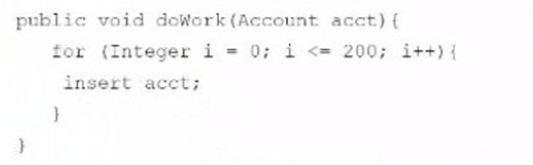
A. Accounts are inserted.
B. Account Is inserted.
C. 200 Accounts are inserted.
D. 201 Accounts are Inserted.
Explanation:
Loop Analysis:
1. The loop runs from i = 0 to i <= 200, which means it executes 201 times (not 200, because it includes both 0 and 200).
2. Each iteration performs an insert acct operation, inserting the same Account object repeatedly.
Governor Limit Consideration:
1. Salesforce enforces a DML governor limit of 150 statements per transaction (in synchronous contexts).
2. This code attempts 201 DML operations, which would exceed the limit and throw a LimitException.
3. However, the question asks what the code does (not whether it succeeds), so the correct answer is based on the loop logic.
Why Not Other Options?
A) Accounts are inserted → Too vague; the question asks for the exact count.
B) Account is inserted → Implies only one insertion, but the loop runs 201 times.
C) 200 Accounts are inserted → Incorrect; the loop runs 201 times (i <= 200).
Key Takeaway:
The code attempts to insert 201 Accounts but would fail due to governor limits.
If this were a real scenario, you’d need to:
. Move the insert outside the loop (e.g., bulkify with a list).
. Or use i < 200 to limit iterations to 200.
Reference: Salesforce Governor Limits
| Salesforce-Platform-Developer Exam Questions - Home |
| Page 2 out of 37 Pages |